Identity Lifecycle Management
Lifecycle Managementbuilt for real environments
Automate joiners, movers, and leavers across every app and identity source in dynamic, real-world environments.
Identity Lifecycle Management
Automate joiners, movers, and leavers across every app and identity source in dynamic, real-world environments.
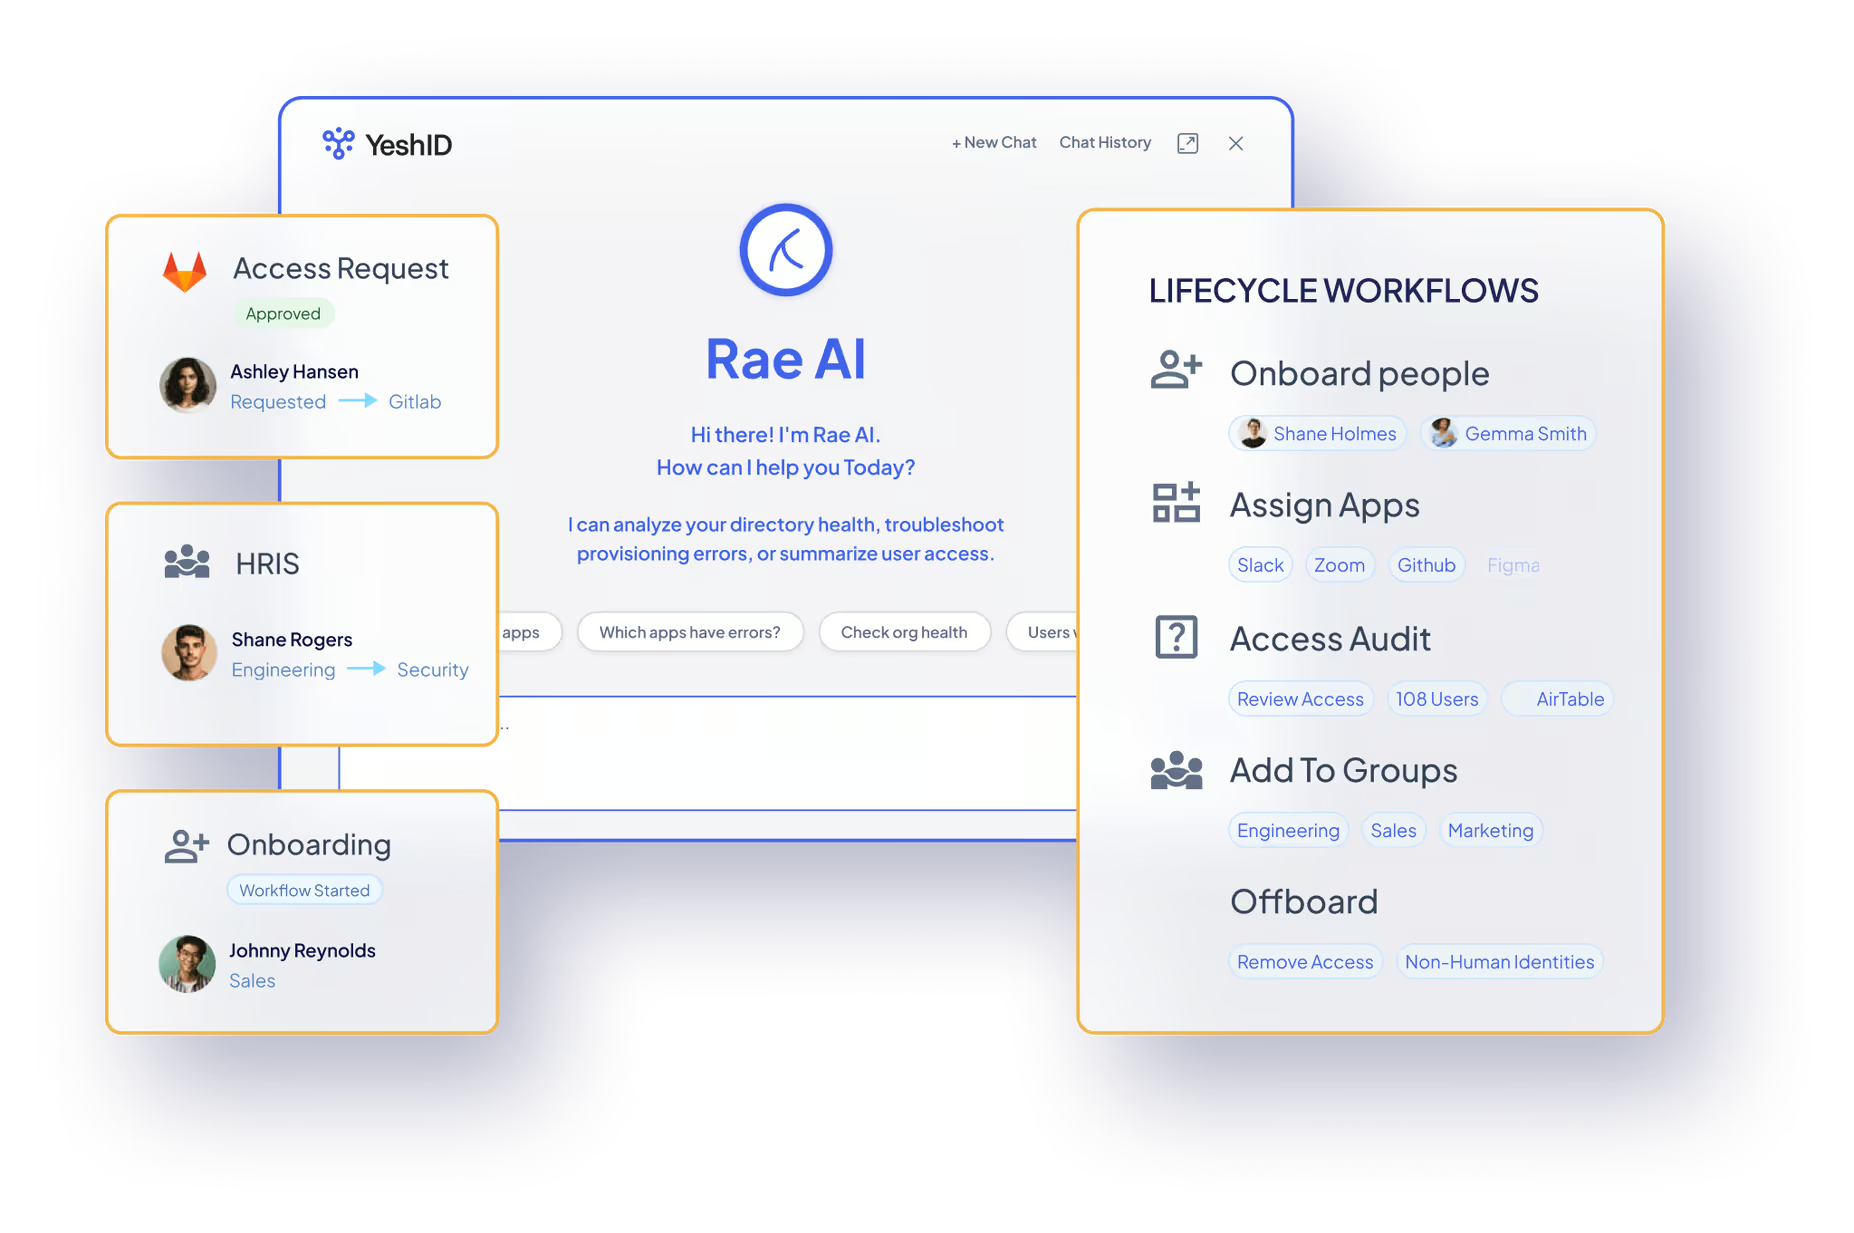
YeshID manages identity lifecycles as a continuous process, not a one-time HR event. It connects directly to your real sources of truth, tracks change over time, and enforces access based on current state rather than outdated assumptions.
YeshID listens to HRIS systems, directories, and identity providers to detect when someone joins, changes roles, or leaves. Lifecycle actions are triggered by actual events, not brittle scripts or manual checklists.
Instead of locking access into rigid roles or groups, YeshID continuously evaluates user attributes and context. When a title, team, or employment status changes, access updates automatically across connected systems.
Temporary access changes are inevitable. YeshID treats them as first-class events with time bounds, approvals, and visibility so short-term exceptions do not become long-term risk.
Offboarding is more than disabling a single account. YeshID removes access across SaaS apps, APIs, tokens, and non-human identities, even when access was granted outside your primary identity provider.
Every lifecycle action is logged, explainable, and auditable. You can see what access was granted or removed, which policy triggered it, and who approved it without reconstructing events from tickets or spreadsheets.
Find out what your people and software can really reach.